Securing the Information Behind Mission-Critical Government Services

Headshot of three webinar speakers on blue background

The true test of government technology isn’t how it performs on an ordinary day. It’s what happens when something goes wrong.

Cyberattacks, natural disasters and other disruptions can quickly put both information and essential services at risk. To maintain continuity, agencies need to think beyond traditional cybersecurity and connect security, information governance and recovery planning, ensuring trusted information remains available to the people who need it, even during a crisis.

During a webinar hosted by Laserfiche and Government Technology, speakers discussed how agencies can prevent service disruption and build trust with residents.

Built-In Security

Security is much harder to bolt on than to build in.

“Innovation and security are not opponents,” Liana Bailey-Crimmins, the former California state CIO and current CIO for Covered California, said on the webinar. “Through security, we can ensure that innovation lasts.”

When agencies wait until after technology decisions have been made to address security, they risk creating gaps, delays and additional work. Bringing security teams into the process earlier allows agencies to establish access requirements and other safeguards from the start.

Encryption, configurable access controls and audit logs help agencies safeguard sensitive information, while geographic redundancy supports recovery when disruptions occur. Clear agreements with cloud providers are equally important, ensuring both sides understand who is responsible for security, continuity and recovery.

Reliable Essential Services

A backup can restore information, but it doesn’t necessarily restore a service.

Government employees may also rely on identity systems, integrations, vendors, approvals and even manual steps to get essential work done. If any one of those dependencies is unavailable, restoring a repository or server may not be enough to get services running again.

“Resilience is not what the architecture promises. It’s what the organization can demonstrate under pressure,” said Andy MacIsaac, senior strategic solutions manager for government and education at Laserfiche.

Creating Consistent Governance

Governments know they need to strengthen governance for data, AI, and critical systems and solutions. But that is challenging when information is scattered across repositories and departments follow different processes. Every additional system creates another place to manage permissions, apply retention rules and produce evidence for audits.

Agencies can simplify that environment with common processes for classifying information, routing work, enforcing access and retention requirements, and preserving an audit trail. Consistency doesn’t mean treating every piece of information the same; agencies can apply stronger controls where sensitivity or risk requires them.

Governance only works when employees can work with it. If the approved way to find, access or share information creates too much friction, staff may turn to faster — and potentially less secure — workarounds. Effective governance should make the secure path the practical path.

A unified approach to information management can help agencies put these principles into practice without adding complexity to employees. By connecting information across departments and existing systems, agencies can automate routine workflows, apply security and retention policies consistently, maintain complete audit trails, and give authorized staff reliable access to the records they need. The result is less administrative burden, fewer information silos and a stronger foundation for compliance, continuity and responsive public service.

“I think everyone is trying to strengthen their governance right now,” said Joe Morris, chief innovation officer at eRepublic. “The challenge is doing so without adding more tools or administrative work.”

Start with One Essential Service

Resilience doesn’t have to begin with an agencywide transformation. It can start with one service that simply cannot afford to fail.

“Public trust is earned when services keep working when the storm is at our door,” Bailey-Crimmins said.

To get started, choose an essential service and run an information resilience drill around it. Identify the information required to deliver it, who needs access, which systems and vendors it depends on, and what happens when one of those dependencies becomes unavailable.

Then test the recovery path with the people who actually deliver the service. Can they access the information they need? Do integrations and handoffs still work? Can they continue serving residents within an acceptable timeframe?

The exercise turns resilience from an abstract goal into something agencies can see and improve. It should produce a clear picture of where the gaps are, who is responsible for addressing them and what needs to change.

Just as importantly, it creates a repeatable approach. Agencies can take what they learn from one essential service and apply it to the next, building resilience one critical process at a time.

Hear directly from Liana, Joe and Andy on how to modernize large-scale, mission-critical governmental operations with governed agentic AI and enterprise security.
New Laserfiche AI Innovations! – January

Info-tech Live New Orleans

Join over 400 IT professionals to explore how exponential technologies are transforming organizations.

12th American Digital AI, Tech, & Business Congress

You will not be replaced by AI, you will be replaced by a professional who is 100x more productive because they know how to use AI; organizations will be displaced by those that have incorporated AI agents into their critical processes and migrated toward Web3 technologies.

Join +5,000 C-Levels (CEOs, CDOs, CIOs, CMOs, CTOs, CISOs, CFOs), and AI, IT, marketing, development, Innovation, digital transformation, and eCommerce professionals from the Americas. Share experiences to face the 6th Technological Revolution, achieve the equivalent of an MBA in digital technologies, and close more business in 2 days than in 1 year during the Congress.

AI World Conference

ARE YOU READY FOR THE 6TH TECH REVOLUTION? Join global tech providers and C-Levels from +100 countries.

Empower 2027 Expert: Tips to Make the Most of Your Experience

The Importance of Information Readiness in Building the Next Decade of Digital Government

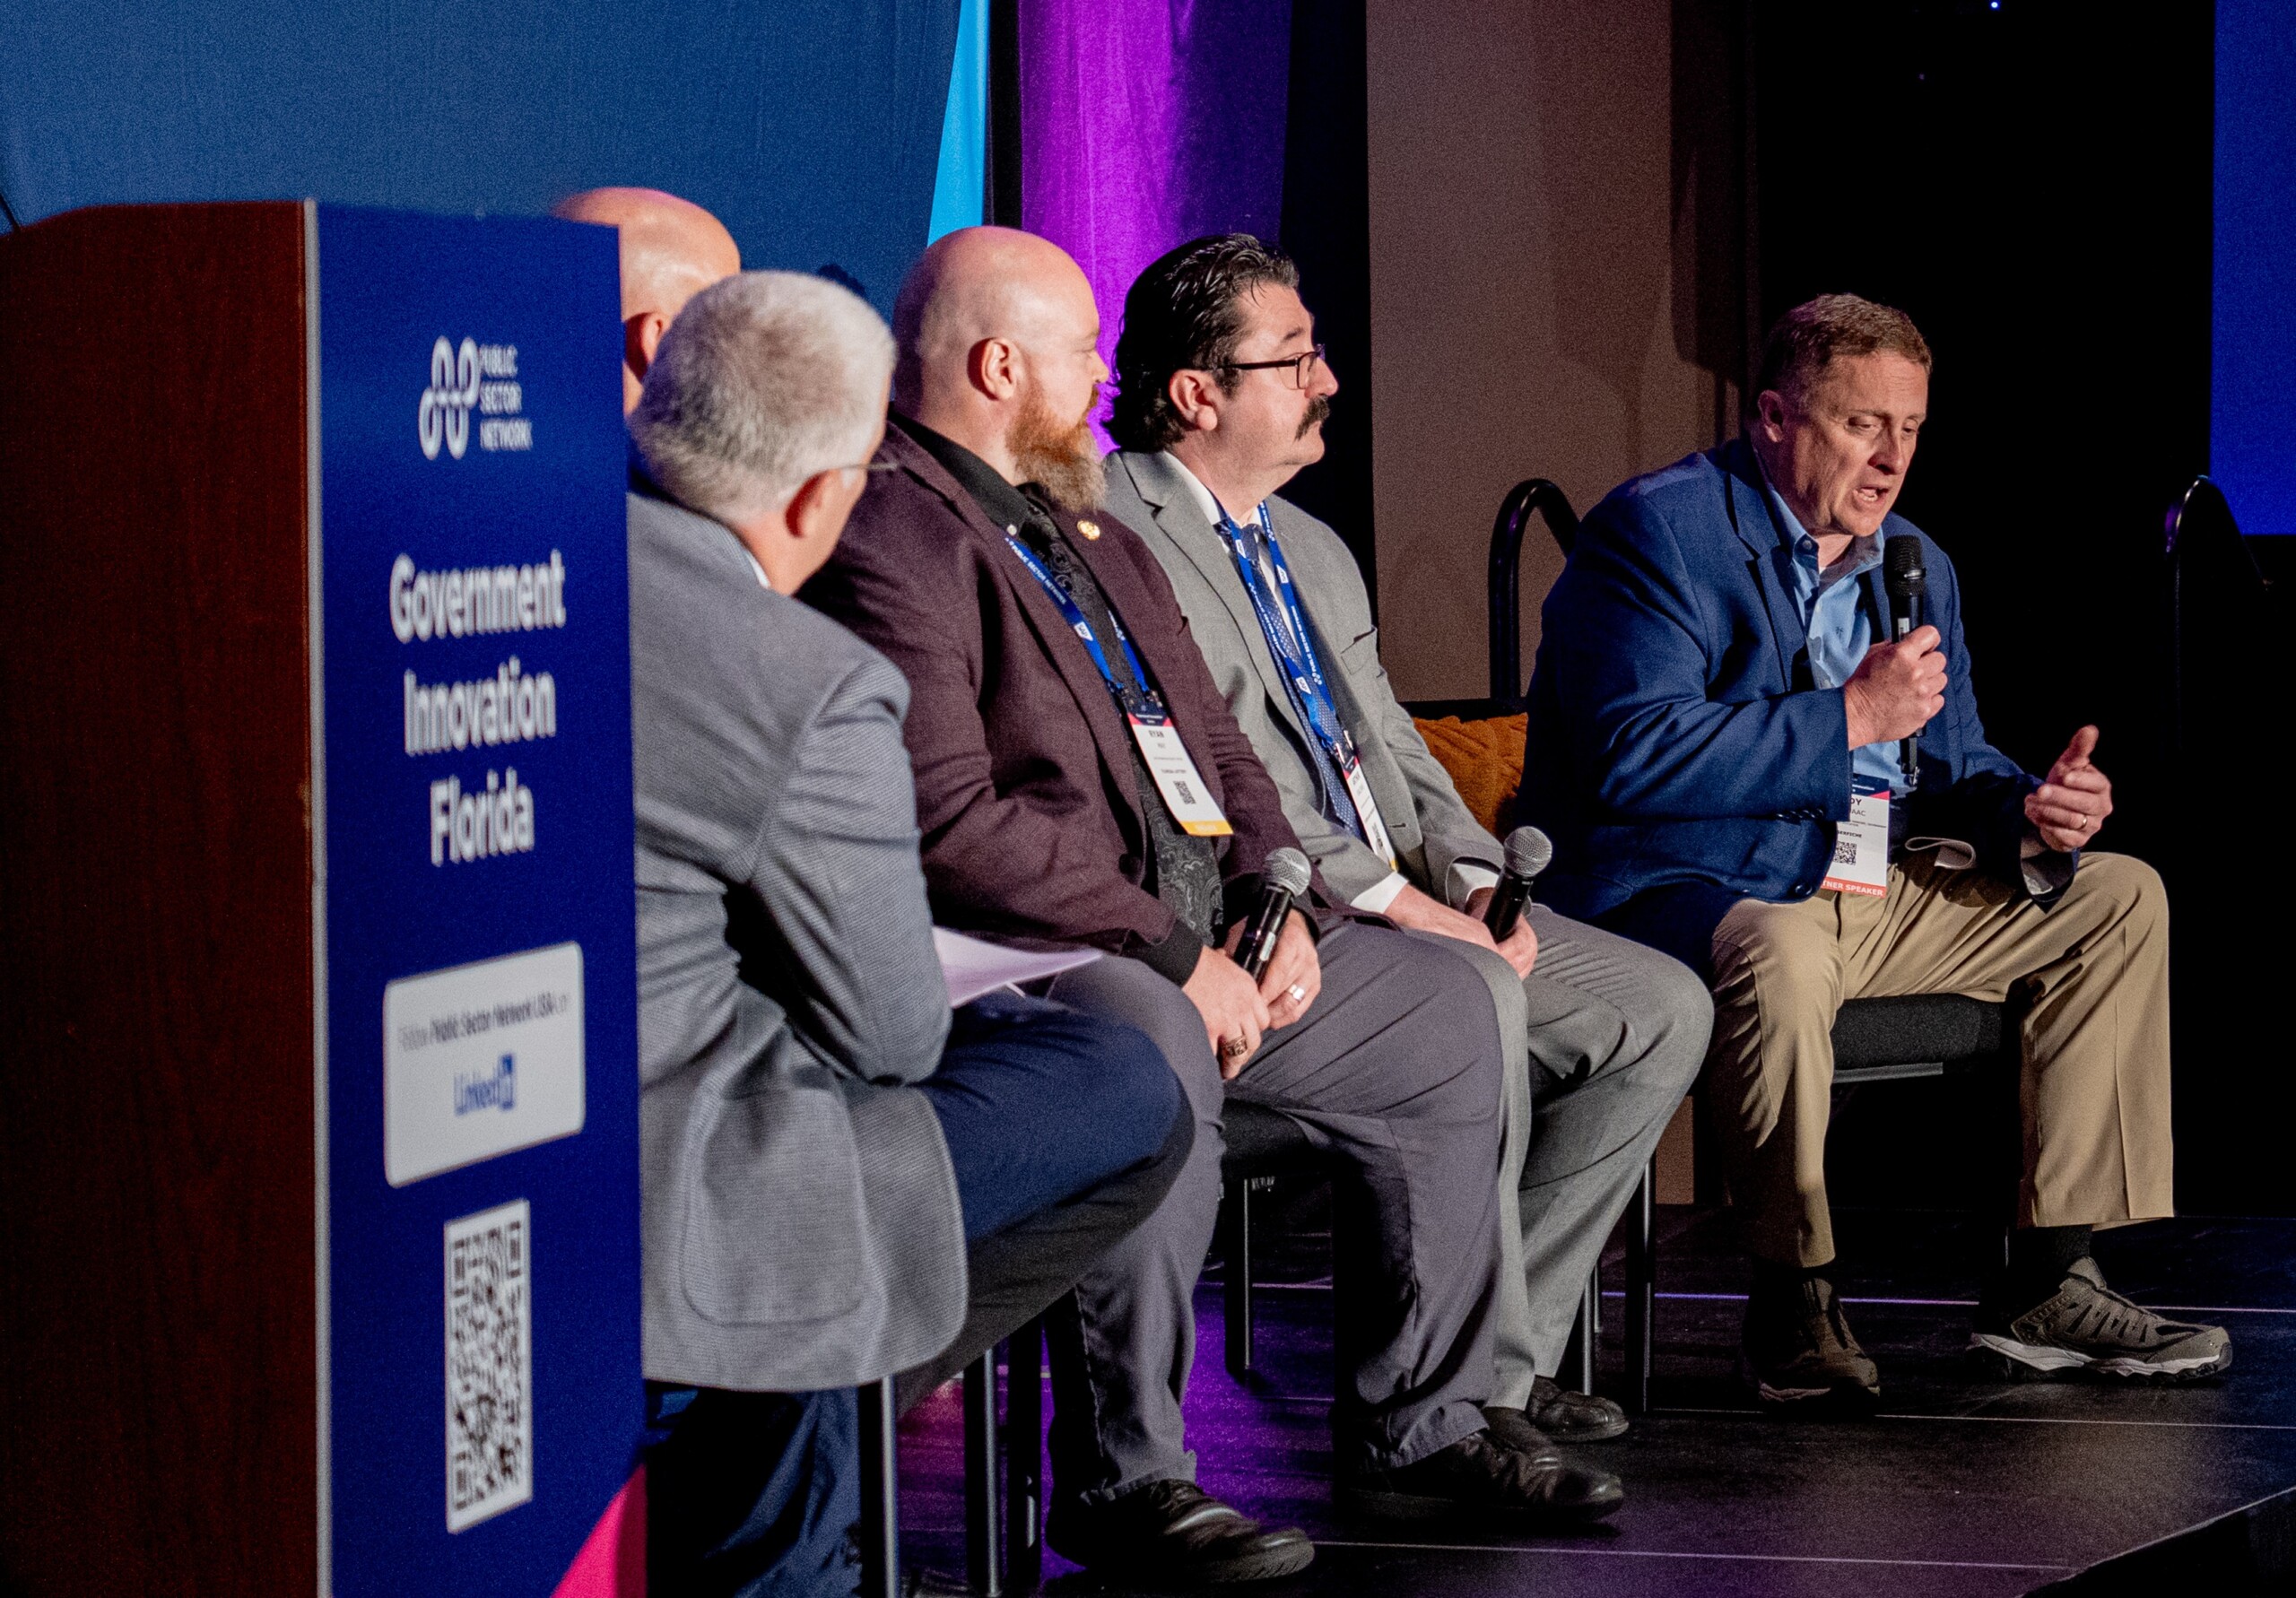
PSN Florida panel on stage

At the Government Innovation Showcase in Florida, state leaders gathered to discuss modernizing services, advancing digital transformation and the importance of cross-agency collaboration. With the theme “From Intent to Impact: Building Florida’s Next Decade of Digital Government”, the event facilitated networking opportunities and provided agency leaders time to hear real-world examples of strategic AI initiatives.

Eric Graham, State Chief Data Officer of Florida Digital Service, delivered the keynote “Preparing Florida for the Next Decade of Digital Government” with a statement relevant for all government leaders:

“AI readiness isn’t actually an AI problem. It’s a data problem.”

That observation gets to the heart of a challenge facing state and local governments today.

For the last decade, government modernization has largely focused on digital transformation. Agencies digitized records, automated forms, moved applications to the cloud and made services available online. Now, as agencies accelerate towards intelligent automation, the role of a secure and trusted data environment becomes foundational. Government agencies must evolve to operate effectively in an AI-enabled world. Florida is evolving its data approach to support enterprise-wide alignment as we enter the era of intelligent government.

Graham offered important insight for AI-driven government leaders: If information is fragmented, AI operates on that fragmentation. If definitions differ between agencies, AI doesn’t scale. If information can’t be trusted, neither can any decisions based on that data.

Small Digital Changes, Big Public Impact

We continued the discussion of AI’s impact on information readiness in a panel called ”Small Digital Changes, Big Public Impact.” Joined by Ryan May, CISO of the Florida Lottery; Arthur Bialowas, CISO of Florida A&M University; and Chris Welch, the Assistant Director/Lieutenant Colonel, Department of Financial Services / Criminal Investigations Division in Florida, we discussed the need to start with impactful use cases in order to find the measurable impact of AI initiatives.

In complex public sector environments, targeted digital workflows can strengthen service delivery and system performance without large-scale disruption. Often, incremental modernization reduces operational and cybersecurity risk while accelerating digital maturity—without disrupting critical services. Florida’s CIO also recently participated in The 2026 NASCIO State CIO Survey | The State CIO in Motion: Priorities, Pressures and Progress, which confirms Florida is on the right path. NASCIO’s survey explores how state CIOs navigate digital services, technology investment governance, AI, IT accessibility and technology. The results confirm Florida’s strategy: 78% of state CIOs reported they adopted an AI governance framework and 77% are using AI in inventory and documenting uses in agencies and applications, an increase from 2025.

Florida, Graham and our panelists are all in agreement: AI investment includes data governance and information readiness.

Any government agency evaluating their own readiness for the era of intelligent government should review their documents and content and ask the following questions:

  • Is information accurate and discoverable?
  • Is it governed throughout its lifecycle?
  • Can employees securely access the right information when they need it?
  • Can information move between processes and systems without losing its context?
  • Can an agency demonstrate who or what system accessed sensitive information and what they did with it?
  • Are audit reviews and cyber protocols integral parts of data governance?
  • Those questions become increasingly important as AI moves from experimentation into operational government.

Secure, Holistic, Interoperable, Networked, Ethically Managed and Discoverable

As part of Florida’s emerging data strategy, they’ve also defined the ideal state for data as secure, holistic, interoperable, networked, ethically managed and discoverable—their SHINED principles. This federated approach is built around collaboration, interoperability and shared capabilities.

For years, modernization has largely optimized what happens inside agencies, but intelligent government requires improving what happens between them. Citizens don’t experience a permitting database, document repository, ERP system and workflow application; they experience their interaction. The technology architecture may be fragmented, but the citizen experience cannot be.

Modernize the Information Layer

This is also why modernization doesn’t always have to begin with replacing core systems.

Most Florida agencies have made substantial investments in mission-critical applications such as ERP, financial, permitting and GIS. Those systems contain important data and support essential functions. Now, there are opportunities to make the information surrounding those systems work more intelligently.

Platforms such as Laserfiche can provide an information and process layer across existing environments—connecting content with automated workflows in a governed environment.

Florida’s Justice Administrative Commission offered a practical example at the event. Long before today’s AI conversation, the agency moved away from paper-intensive processes with Laserfiche. When COVID suddenly forced employees to work from home, that digital foundation helped the agency continue to support Florida’s justice system. What looked like document modernization became operational resilience. The same principle applies to AI today.

Keep Pace or Drive Innovation? Build the Foundation Before the Next Technology Arrives

One of the most interesting things I heard in Florida was that the next decade of government won’t be defined by the technologies agencies adopt, but by the institutional capabilities they build. I think that’s exactly right.

AI will change. Models will change. Applications will change. The next breakthrough technology will eventually arrive. Through all the changes, government agencies will still need to take responsibility for protecting constituents’ information and maintaining public trust.

The agencies that lead in the AI era won’t be those that deploy AI first but the ones that can connect information across organizational boundaries, govern it throughout its lifecycle, protect it without limiting its use and turn it into public value.

That’s the foundation of intelligent government.

When a government leader considers the next AI initiative, they shouldn’t ask themselves, “Which AI should be deploy?”

The question should be much simpler:

“Is our information ready?”

If you’re ready to hear the best practices of information readiness and learn how to confidently modernize mission-critical operations with a secure, cloud-based content management platform designed for today’s security and compliance challenges, listen in now.

Advancing CJIS-Ready Cloud Operations with Enterprise Security

Speaker at podium with CJIS logo on blue background

Moving to the cloud is a very different proposition when you’re responsible for criminal justice information, whether that includes fingerprints and other biometric data, criminal histories, case records or information about property associated with a crime.

Law enforcement agencies and other organizations subject to CJIS (Criminal Justice Information Services) requirements want the flexibility and operational advantages of the cloud. Yet, they have little room for uncertainty about if or how sensitive information is protected, who can access it or what happens when a critical system goes down.

That sets a high bar for cloud security. And it provides useful context for the launch of Enterprise Security, a new suite of capabilities designed to help organizations securely modernize mission-critical operations in Laserfiche Cloud.

Enterprise Security addresses CJIS and GovRAMP security requirements based on the NIST SP 800-53 framework. It also introduces additional protections against emerging threats while strengthening the controls organizations rely on to keep critical information secure and available.

What Does CJIS Readiness Look Like in Practice?

CJIS readiness isn’t defined by a single security feature. Agencies need to consider how they protect criminal justice information throughout their environment and configure technology around their own requirements.

For IT and security teams, that raises practical questions:

  • Who can access sensitive information, and how do we manage inactive sessions?
  • Can we see what users and privileged accounts are doing across the system?
  • How quickly can we recover if the region hosting our repository becomes unavailable?
  • Are integrations and automated processes maintaining the protections we put in place?

The last question is particularly easy to overlook. Agencies rarely use an information management platform in isolation. Often, other applications supply information to Laserfiche or retrieve information from it. Automated processes can connect those systems without someone manually moving a document from one place to another. For example, a workflow might route case-related information between systems or make a record available to an authorized user as part of an investigative or administrative process.

Those connections need the same security discipline as the applications themselves. Access should be limited to the information that’s necessary for each user and their role, and protections shouldn’t be lessened or disappear simply because a process has been automated.

Enterprise Security strengthens that environment with enhanced encryption using FIPS 140-3 compliant cryptographic algorithm modules. Configurable inactivity timeouts give organizations greater control over how long sessions remain active, complementing existing capabilities such as role-based access controls and single sign-on.

Together, these technology controls support CJIS security requirements. Agencies remain responsible for understanding the information they manage, configuring their environment appropriately and demonstrating that they meet those requirements in practice.

Seeing Beyond the Repository

Security teams also need to know what’s happening around their information.

Repository audit logs provide a record of activity involving content. Enterprise Security expands that view through an advanced audit trail that covers activity across the system, including user and account security events. Support for integration with SIEM and log aggregation tools allows that activity to become part of the organization’s broader security monitoring.

That wider view is valuable when an agency needs to investigate unusual behavior or review changes to an account. If an administrator’s permissions change unexpectedly or an account begins accessing information it normally doesn’t, security teams need a record of those events alongside activity involving the content itself. It also helps organizations demonstrate that the controls they have in place are working as intended.

For teams managing sensitive information, comprehensive visibility provides a clear record of how people interact with the system, from the access they have to the actions they take.

Preparing for the Outage You Can’t Prevent

Some security events begin with malicious activity. Others begin when infrastructure simply becomes unavailable. Either way, a public safety agency can’t afford to lose access to critical information for an extended period. A regional outage can quickly become an operational problem if criminal histories, identity or case records are unavailable.

Multi-region disaster recovery helps organizations prepare for regional outages, with near real-time account-level replication to support recovery. If a critical issue affects one region, the repository can be brought back online with disaster recovery support. Automated four-hour repository data snapshots provide an additional recovery capability.

This is one of the more consequential ideas behind Enterprise Security. Disaster recovery isn’t separate from protecting mission-critical information. Availability is part of the security commitment.

For agencies evaluating cloud environments through a CJIS lens, that changes the conversation from simply preventing an incident to asking how operations continue when prevention isn’t enough.

Security Threats Aren’t Standing Still

The environment agencies are defending is changing too. AI has introduced questions about how organizations govern the tools they choose to use. It’s also changing the nature of some security threats by making automated activity easier to scale, adapt and target.

Some of these threats are new, while others are longstanding attack methods becoming more sophisticated. Unauthorized AI bots generate large volumes of automated activity, while DDoS attacks increasingly use automation to vary tactics and make malicious traffic harder to distinguish from legitimate use. Both can overwhelm systems and disrupt availability. Laserfiche Cloud includes protections against these types of threats and can adapt over time.

Setting a Higher Bar for Cloud Security

For agencies working toward CJIS readiness, evolving threats add to an already high security bar. They need technology that protects sensitive information as applications connect and processes become automated, without creating so much friction that employees find ways around it. They also need a path back to normal operations when something unexpected happens.

Enterprise Security was built to strengthen that underlying architecture in Laserfiche Cloud, supporting rigorous security requirements while helping agencies prepare for what comes next.

Stronger cloud security creates room to modernize with greater confidence while maintaining the protections required for criminal justice information.

The standard is high because the information demands it.

Learn key considerations of establishing long-term enterprise resiliency by downloading the Operational Guide to CJI now.

Top Predictions for Agentic AI Readiness and Governance in 2027

New Laserfiche AI Innovations! – October