


Enhance your workflows for document processing and import! In this hands-on lab, we’ll explore complex workflow solutions for bulk document import and re-processing repository documents.
Streamline data processing with Workflow! In this hands-on lab, we’ll explore complex workflow solutions for working with batches of data.
Join this hands-on, instructor-led virtual training to automate records management and data retention in Laserfiche.
Join this hands-on, instructor-led virtual training to enhance metadata templates and fields and dive into more administrative features.
Elevate your form and process design! This hands-on lab will show how to build sophisticated forms and processes to enhance user experience and process maintenance.
Designed for new users to get caught up on Laserfiche administration basics, this lab-style instructor-led training will provide the foundations necessary to successfully manage, administer, and troubleshoot your Laserfiche system. Topics covered include repository design, metadata administration, repository security and records management, along with repository and task automation.
Dynamic Fields Now Support External Lookups
Dynamic fields are a useful tool for making your repository metadata cleaner, more consistent, and easier to manage, strengthening data integrity across Laserfiche. This month, we’ve introduced new updates that expand the capabilities of dynamic fields to make them even more powerful.
Previously, dynamic fields were limited to data sourced from static lookup tables. Now, you can configure dynamic fields using data query and web request rules, allowing you to pull live values from external applications directly into your metadata in real-time.
This update allows dynamic fields to display field value options that are based on live business data, reflecting the most current information instantly, no matter where it is stored.
In addition, dynamic field configuration is now available within the template designer, providing a more intuitive place to create and manage these connections.
Together, these updates offer new ways for teams to keep their repository metadata accurate, current and synchronized across their line-of-business systems.
Improve AI Data Capture with Dynamic Fields
Smart Fields can now use list options supplied by dynamic fields to guide metadata extraction. By checking extracted values against the currently available options, Smart Fields can produce more consistent metadata that aligns with an organization’s approved data. Organizations can continue managing these options in their existing source, without duplicating this information in each Smart Fields prompt.
Expanded Audit Trail Events
Laserfiche Cloud Audit Trail is expanding to provide broader visibility into security-sensitive and administrative activity across your cloud environment. Administrators can now better review privileged actions, identity-related changes and account administration activity from a centralized place.
This expansion includes team and project activities along with account-level security and user events. This allows organizations to extend audit visibility beyond the repository into process automation and account-level operations. With a clearer record of what happened and when, it’s now easier to monitor critical account activity and troubleshoot issues for faster investigation and clearer oversight.
Other updates:
Laserfiche Forms Mobile App Update: You can now sign into the Forms mobile app on your iOS or Android device using fingerprint or facial recognition. Biometric authentication now supports Single Sign-On (SSO) for Laserfiche Cloud, including SAML and AD FS authentication. This update also supports a deep linking feature that allows you to open the app directly to a specific form, making it easier to access the right form faster.
Repository API update: The Repository API now supports new capabilities for interacting with documents and metadata, including the ability to manage access rights, document annotations, records management and users’ Recent Documents, Starred documents and personal Collections. See the full changelog for more details.
Idle Session Termination: Administrators can now enable idle session timeout to automatically sign users out after a selected period of inactivity. This gives organizations greater control over session security and helps protect information when a signed-in device is left unattended.
New Toolkit for Developers: Explore the new LF Form Builder, which includes a toolkit of resources and examples to help you modernize how you build, test, and maintain Laserfiche Forms customizations. Learn more about the resource here.
New security suite extends Laserfiche’s proven security controls and adds near real-time data replication for governments, law enforcement and security-conscious enterprises.
LONG BEACH, CALIFORNIA, Aug. 6, 2026 — Laserfiche — the leading SaaS provider of intelligent content management — today announced the launch of Enterprise Security, an advanced suite of security enhancements designed for organizations navigating complex regulatory environments. Enterprise Security addresses GovRAMP and CJIS (Criminal Justice Information Services) security requirements based on the NIST SP 800-53 framework. For organizations handling privileged citizen, legal or corporate data, these built-in controls streamline audit preparation and fortify defenses.
With organizations placing a higher priority on data stewardship and corporate governance, enterprise IT leaders require a security architecture that protects data without slowing down operations. Laserfiche Enterprise Security extends Laserfiche Cloud’s highly resilient infrastructure with multi-region data replication, elevated security controls for privileged accounts, and built-in governance safeguards.
“Maintaining data integrity and compliance has always been at the heart of Laserfiche’s operations,” said Michael Allen, CTO at Laserfiche. “With Enterprise Security, Laserfiche provides enterprise IT users, especially those in government, law enforcement and highly regulated industries, with the complementary controls designed to meet stringent information security standards and protect their most sensitive assets.”
High-Security Controls and Regulatory Alignment
Laserfiche Enterprise Security introduces multi-region disaster recovery, enhanced oversight capabilities, and government-ready cloud security controls tailored for mission-critical data and sensitive operations.
Key capabilities included with Enterprise Security:
- GovRAMP and CJIS Readiness: Deploys advanced operational controls designed to meet strict government and criminal justice compliance mandates for sensitive data handling.
- Multi-region disaster recovery: Safeguards critical operations against large-scale infrastructure failures with near real-time, account-level repository data replication and multi-region failover.
- Advanced audit tracking and analytics: Provides complete visibility into user login activity, system changes, and security events
- Proactive threat augmentation: Bolsters existing security measures by adding specialized protections against unauthorized AI bot scraping and distributed denial of service (DDoS) attacks.
Laserfiche is listed on the GovRAMP Progressing Product List, with the Enterprise Security suite delivering the architectural controls required to support these standards.
Tailored for Mission-Critical Operations
Enterprise Security is built for organizations that safeguard heavily regulated and sensitive data, where seamless recovery and strict information control are vital to everyday operations:
- Government agencies and law enforcement: Safely manage records and criminal justice information while strictly adhering to CJIS and GovRAMP standards.
- Large enterprises and financial services: Protect proprietary corporate data and client financials with strong cryptographic modules and advanced visibility into user activity.
“Highly regulated sectors, from law enforcement to state and local governments, face a unique challenge: They must modernize content management while upholding non-negotiable security standards,” said Andrea Malick, principal advisory director at Info-Tech Research Group. “Solutions that offer built-in compliance frameworks like CJIS and GovRAMP give enterprise IT buyers the confidence to migrate sensitive workloads to the cloud without compromising control.”
Pricing and Availability
Enterprise Security is available starting today as a supplemental SKU for qualifying Laserfiche Cloud deployments.
Laserfiche is also introducing Business+, a new comprehensive subscription tier designed for organizations that want high-level security capabilities built directly into their standard platform deployment.
For More Information
- For a deep-dive into Laserfiche security and governance, visit laserfiche.com/products/trust-security.
Enterprise Security
We’re excited to introduce Laserfiche Enterprise Security, a suite of advanced compliance and data protection tools built directly into Laserfiche Cloud as an add-on for qualifying customers. The new add-on is designed to help organizations reduce risk, improve operational resilience and confidently manage their most essential information.
Laserfiche Cloud has always been built on a secure foundation, and Enterprise Security extends that for organizations who may have elevated security and compliance requirements.
For agencies handling Criminal Justice Information and state, local and tribal governments, along with other regulated public entities, Enterprise Security removes a major barrier to cloud adoption with a NIST 800-53–backed, CJIS-ready, GovRAMP-aligned environment.
Key Features:
Enhanced Disaster Recovery
Enterprise Security introduces cross-regional disaster recovery with four-hour snapshots, helping organizations recover faster from regional outages while maintaining data residency requirements. This reduces downtime, improves business continuity and gives IT teams greater confidence that critical services can keep running when they’re needed most.
CJIS and GovRAMP
Enterprise Security includes CJIS-ready operational controls and an environment built to GovRAMP standards. These frameworks align with U.S. NIST standards and are designed to help agencies modernize operations with Laserfiche Cloud while supporting key security controls that may be required for compliance.
See all that’s included with Enterprise Security on our Trust & Compliance Page, and register for our upcoming webinar to learn more.
NEW Business+ Tier
We have added a new enterprise tier that includes Enterprise Security along with expanded storage, additional API capacity, increased AI usage, more workflow resources and a dedicated sandbox environment for testing and validating changes before deployment. It’s built for organizations that need enterprise-scale performance, flexibility and security as they continue to grow.
Business+ includes Enterprise Security and:
- Expanded cloud storage
- Increased API capacity
- More AI usage
- Additional workflow resources
- A dedicated sandbox environment for testing and validating changes before deployment
Learn more about what’s included on our pricing page.

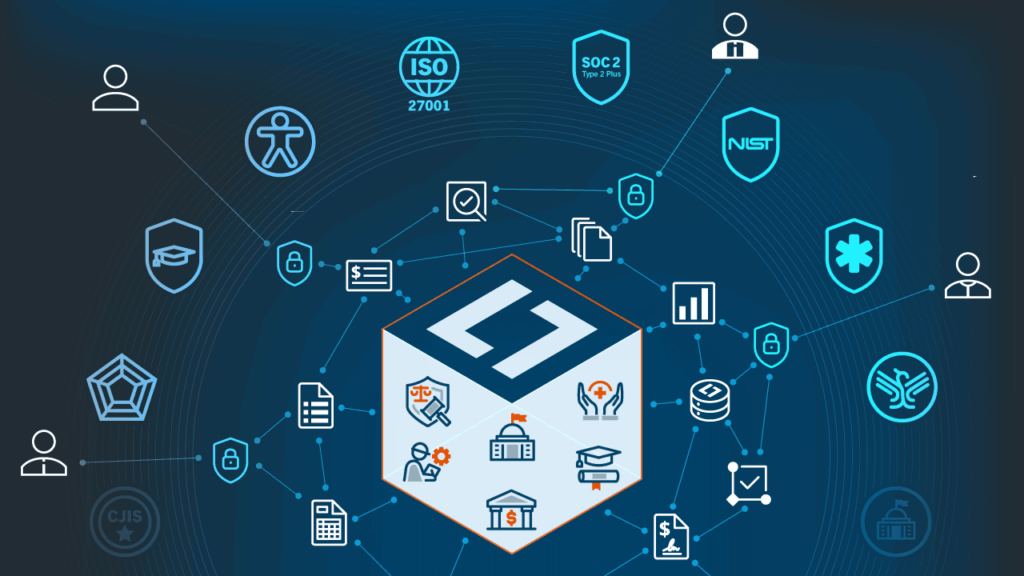
Security Certifications and Compliance Frameworks
GovRAMP
Pending
Laserfiche will achieve GovRAMP Verified status, demonstrating its implementation of security controls aligned with GovRAMP and NIST SP 800-53.
Contact us for more information.
CJIS Ready
Laserfiche Cloud supports CJIS-ready controls that help organizations securely manage Criminal Justice Information (CJI). Enterprise Security provides enhanced auditing, monitoring, encryption and administrative controls that address CJIS and other security requirements.
Contact us for more information.
SOC 2 Type 2 Plus
This report details the controls for Laserfiche Cloud related to the criteria for the security, availability and confidentiality principles set forth in TSP section 100, 2017 Trust Services Criteria for Security, Availability, Processing Integrity, Confidentiality, and Privacy (AICPA, Trust Services Criteria). To view a copy of this report, please contact us.
ISO/IEC 27001:2022
Laserfiche has obtained the ISO/IEC 27001:2022 certification for its information security management system (ISMS) within the scope defined by its Statement of Applicability, covering its suite of SaaS and self-hosted enterprise content management and process automation applications.
HIPAA
Laserfiche’s SOC Type 2 Plus covers the security requirements set forth in the Health Insurance Portability and Accountability Act of 1996 (HIPAA), provided within Title 45 Code of Federal Regulations Sections 164.308 – 312 (45 CFR Sections 164.308-312) (the Security Requirements).
Web Content Accessibility Guidelines 2.2 AA
Laserfiche has published VPATs and ACRs available for all Laserfiche Cloud and self-hosted products. Alignment to the WCAG 2.2 Level AA standard is the basis of our approach to compliance with Section 508 and EN 301 549 requirements. See accessibility details…
DoD 5015.2
DoD 5015.2 details the Department of Defense’s baseline requirements for Records Management Applications (RMA), that facilitate adequate and appropriate basis for addressing the basic challenges of managing records in the automated environment that increasingly characterizes the creation and use of records. Laserfiche Cloud records management controls are based on our self-hosted Department of Defense 5015.2 version 3-certified electronic records management capabilities.
SEC Rule 17a-4
Laserfiche features support non-alterable record archival requirements such as WORM (write once, read many) used to address SEC Rule 17a-4 for broker dealers. Beyond financial services, Laserfiche’s controls can also be applied to support records management practices for electronically stored information (ESI) requiring prevention of any unauthorized alternations or deletions of digital records.
HECVAT
Laserfiche has completed the Higher Education Community Vendor Assessment Toolkit (HECVAT) questionnaire. Contact us for more information.
NIST 800-53
Laserfiche security controls are aligned with NIST 800-53.
AI Security and Governance
Laserfiche AI services are provided using AI models and services from OpenAI. For information on AI services in regions where OpenAI is not available, please contact us.
Regional data privacy requirements
Laserfiche AI addresses privacy and security standards of our current data center locations supporting GDPR (EU), CCPA/CPRA (USA), and PIPEDA (Canada) for low to moderate risk data. Our AI features are architected to support regional and industry-specific compliance needs, providing the same level of data sovereignty and protection you expect from Laserfiche Cloud.
For more information related to Laserfiche AI and data privacy, refer to the following:
- Laserfiche Privacy Notice
- OpenAI Security & Privacy
You own your data
- You retain ownership of inputs you provide. While Laserfiche owns the intellectual property rights to the outputs generated by our AI tools, we grant you a broad license to use those outputs for any of your organization’s internal business needs.
- Laserfiche does not use your organization’s data to train any internal or external AI models. Your data is used only as needed to deliver services and to meet our legal and regulatory obligations.
Laserfiche AI user prompts
Laserfiche designs its AI features with safety and security as core principles. We manage prompting risks through two layers of protection:
- Prompt-less by design: Many Laserfiche AI features, such as Document Summarization, do not use user prompts, reducing risks associated with accidental or malicious prompting.
- Enterprise-grade safeguards: For features that do accept user input, like Smart Fields and Smart Chat, we employ industry-standard protections against prompt injection. These include input filtering, validation, and other controls that keep prompts and responses within defined, limited boundaries.
Content confidentiality
Your confidential content is not accessible to other customers or unauthorized third parties. Laserfiche distinguishes between two types of data:
- Your confidential content: Laserfiche does not sell your data. Documents, files, and inputs you upload to Laserfiche are your own content.
- Usage and system data: Like most cloud providers, Laserfiche collects limited, high-level usage data (such as feature adoption and system performance metrics) to operate and improve the platform. This data is de-identified and does not include the contents of your documents or AI prompts.
Data retention
- OpenAI may store the prompts you enter or the responses you receive temporarily for up to 30 days to provide services and identify abuse. After 30 days, API inputs and outputs are removed from their systems, unless they are legally required to retain them. For more details, please refer to the OpenAI Services Agreement.

Security Controls
Below are some of the security controls Laserfiche software includes. If you have questions about a particular security solution or control, please contact us directly.
Single sign-on
Laserfiche Cloud supports single sign-on with Active Directory Federation Services (AD FS) and SAML authentication with identity providers such as Okta and Azure Active Directory.
Repository audit log
The Laserfiche Cloud repository audit log includes details of user actions, including viewing, modifying, creating and deleting documents, and similar operations on metadata and other repository objects.
Fine-grained access control
Administrators can use access rights to limit and control access to individual documents and objects. For example, security tags restrict access to documents on a document-by-document basis.
Intrusion detection
Laserfiche Cloud utilizes host-based intrusion detection systems to reduce the risk of data theft by individuals or organizations attempting to gain unauthorized access.
Access rights
Administrators can configure access rights and privileges to limit actions that users can perform across the repository based upon role assignments or group memberships.
AI governance
Laserfiche AI data is encrypted at rest (AES-256) and in transit (TLS 1.2+). Laserfiche does not utilize any of your data to train internal or external AI models.
Password policies
Laserfiche Cloud supports industry-standard password controls, such as password minimum length, complexity and history.
Penetration testing
Laserfiche engages third-party vendors to conduct external penetration testing of the Laserfiche Cloud system.
Vulnerability scanning
Laserfiche performs a vulnerability scan of backend servers that run in the Laserfiche Cloud hosting environment.
Firewalls
Laserfiche Cloud’s firewall configuration settings are regularly reviewed based on industry standards.
Repository application auditing
Laserfiche Cloud supports auditing of both access and modification of objects in repositories.
Enterprise Security
Securely modernize your business-critical work with Laserfiche Cloud.
Laserfiche Enterprise Security enhances security, resilience and governance capabilities for organizations managing sensitive, highly regulated data in Laserfiche Cloud.1 It provides FIPS 140-3 encryption2, privileged-user activity visibility, configurable session controls and multi-region disaster recovery with near real-time account-level replication.
Available to Laserfiche Cloud Business customers as an optional Add On, included with Business+ and offered for eligible Municipal Cloud packages.
Features
- Multi-region disaster recovery with near real-time repository replication
- Four-hour repository snapshots
- Enhanced user and privileged account monitoring
- Configurable security policies including inactivity session time out controls
- GovRAMP Verified and CJIS-ready
| Laserfiche Cloud Security Features | Professional Tier | Business Tier | Business+ Tier |
|---|---|---|---|
| AES‑256 Data Encryption | ✓ | ✓ | ✓ |
| Role‑Based Access Controls | ✓ | ✓ | ✓ |
| Single Sign‑On (SSO/SAML/AD FS) | ✓ | ✓ | ✓ |
| DDoS Protection | ✓ | ✓ | ✓ |
| Unauthorized AI Bot Prevention | ✓ | ✓ | ✓ |
| Administrative and Repository Auditing | ✓ | ✓ | ✓ |
| Configurable Inactivity Timeouts | ✓ | ✓ | ✓ |
| Advanced Audit Trail | Add On | ✓ | ✓ |
| FIPS 140-3 Cryptographic Modules | ✓ 3 | ✓ | |
| Four-Hour Repository Snapshots | ✓ | ✓ | |
| Multi-Region Disaster Recovery Support | ✓ | ✓ | |
| GovRAMP (Pending) | ✓ | ✓ |
- To ensure alignment with regulatory and operational needs, organizations should evaluate their use cases against the acceptable use restrictions in our Cloud Subscription Agreement before making a purchase. ↩︎
- Note: Enhanced encryption uses FIPS-compliant cryptographic algorithms (FIPS 140-3) that utilize up-to-date crypto routines approved by NIST and compiled to help prevent sophisticated attacks on underlying cryptographic algorithms. Enhanced encryption is available for the Laserfiche Cloud U.S. Region. ↩︎
- Items with an orange check-mark (“FIPS 140-3 Cryptographic Modules” and below) are available with the Enterprise Security Add On for Laserfiche Cloud Business customers, included with Business+ and offered for eligible Municipal Cloud packages. ↩︎
“Laserfiche’s compliance tools in the cloud, and knowing that Laserfiche takes security very seriously have been important factors in our decision making.”rn—Andrew McElrath, strategic project manager at Mille Lacs Corporate Ventures
Featured Success Story
Mille Lacs Corporate Ventures Transitions Corporate Operations to Laserfiche Cloud
Mille Lacs Corporate Ventures (MLCV), created by the tribal government of the Mille Lacs Band of Ojibwe, manages the business affairs of the Band.

Laserfiche is committed to privacy.
Our commitment
At Laserfiche, we have embraced a culture of privacy, which includes embedding privacy-by-design in our engineering efforts, and have implemented controls and policies throughout our organization. Laserfiche is a B2B company based in California. The State of California has passed strict, broad privacy regulation through the California Consumer Privacy Act (CCPA) and the California Privacy Rights Act (CPRA) while the General Data Protection Regulation (GDPR) leads the European Union’s privacy efforts. Many other countries, states and territories have implemented privacy regulations as well. Laserfiche endeavors to continually adapt and adhere to ever-evolving regulations that apply to its business.
Operational privacy
Operationally, we strive to keep our stakeholders’ data secure and retain only information we collect from you where we have an ongoing legitimate business need to do so, like providing you with a service you have requested, or to comply with applicable legal, tax or accounting requirements.
Privacy training
At Laserfiche, all employees are required to complete annual privacy training which covers applicable privacy regulations and data handling best practices.
Laserfiche documentation
In addition to what we communicate in our Privacy Notice, our Cloud Subscription Agreement with accompanying Data Processing Addendum specific to the Laserfiche Cloud platform addresses data privacy regulations including GDPR, CCPA and PIPEDA.
International transfers
For personal data transferred from the United Kingdom, the European Union and Switzerland, we provide appropriate safeguards per the Data Privacy Framework. To learn more, visit the “International Transfers” section of the Privacy Notice.
Information we collect
We collect information that you provide directly to us only for legitimate business purposes. For example, when you manage your user profile, participate in interactive features (such as the Contact Us page), request newsletters or other marketing communications, request customer support, enter login information, or otherwise communicate with us. To learn more visit the “Information We Collect” section of the Privacy Notice.
You have the right to opt-out of marketing communications we send you at any time. You can exercise this right by clicking on the “unsubscribe” or “opt-out” link in the marketing emails we send you. To learn more, visit the “How Laserfiche Uses and Shares the Information We Collect” section of the Privacy Notice.
To read our complete Privacy Notice, visit our Privacy Notice page.
Contact Us for Your ECM Needs
Whether you have product questions, support needs or want to partner with us, we’re here to help you on your digital transformation journey. Fill out the form and a Laserfiche team member will be in touch as soon as possible.